Modern ransomware goes after your backups first. How to extend the classic rule with offline and immutable copies, separate credentials and restore tests, so that recovery is a plan rather than a hope.
In short
The 3-2-1 backup rule means three copies of your data, on two different types of storage, with one copy off-site. Against ransomware, add at least one copy that is offline or immutable, protect backup systems with separate credentials and MFA, and test full restores regularly. A backup you cannot restore within your recovery time is not a backup.
Ransomware groups learned years ago that encrypted servers are worthless as leverage if the victim can restore them. So they now look for backup consoles, delete snapshots and encrypt backup repositories before they encrypt anything else. This guide is written by Devies, a Gothenburg-based product and engineering consultancy, for CTOs, IT managers and operations leads who want backups that still work on the worst day. It covers the 3-2-1 backup rule, why it is no longer enough on its own, the extra layers that matter, and how to test recovery.
What is the 3-2-1 backup rule?
The 3-2-1 backup rule is a long-standing rule of thumb for data protection: keep three copies of your data, on two different types of media, with one copy stored off-site.
Definitions:
- A backup is a copy of data that can be restored independently of the original system.
- An offline (air-gapped) backup is a copy that is not reachable over the network when it is not being written to.
- An immutable backup is a copy that cannot be changed or deleted, by anyone, until a retention period has expired.
- RPO (recovery point objective) is how much data, measured in time, you can afford to lose.
- RTO (recovery time objective) is how long a system may be down before the impact is unacceptable.
The rule spreads risk against hardware failure, fire and accidental deletion. The UK National Cyber Security Centre explains its limit in a post on offline backups in an online world: 3-2-1 spreads copies, but does not require any of them to be offline, and a ransomware attacker with network access and the right credentials can reach all three.
Why do ordinary backups fail against ransomware?
Ordinary backups fail against ransomware because they are reachable with the same credentials and network paths the attacker has already captured.
Common failure patterns:
Weakness
What the attacker does
Countermeasure
Backup server joined to the main domain
What the attacker does
Uses stolen domain admin rights to log in
Countermeasure
Separate identity for backup administration
Snapshots on the same storage
What the attacker does
Deletes snapshots before encrypting
Countermeasure
Immutable or offline copies
Cloud backups with long-lived keys
What the attacker does
Uses the key to delete or overwrite
Countermeasure
Retention locks, MFA on deletion, separate account
Backups never fully restored
What the attacker does
Nothing; the restore simply fails on the day
Countermeasure
Regular restore tests with timings
Only data, no system images
What the attacker does
Restore takes weeks because systems must be rebuilt
Countermeasure
Golden images and infrastructure as code
Malware in the backup
What the attacker does
Restored systems are reinfected
Countermeasure
Keep older restore points, scan before restore
The CISA #StopRansomware Guide recommends maintaining offline, encrypted backups of critical data, regularly testing their availability and integrity in a disaster recovery scenario, and keeping updated golden images of critical systems. It also notes that some cloud providers offer immutable storage, while advising caution because immutable storage may conflict with certain regulatory requirements.
How do you build backups that survive ransomware, step by step?
Build ransomware-resilient backups by starting from what the business must restore and how quickly, then adding isolation, protection and testing around it.
- Rank systems by recovery need. Agree RPO and RTO per system with the business. The ERP system and identity provider usually come before the intranet.
- Apply 3-2-1 as the baseline. Three copies, two media types, one off-site, for every critical system.
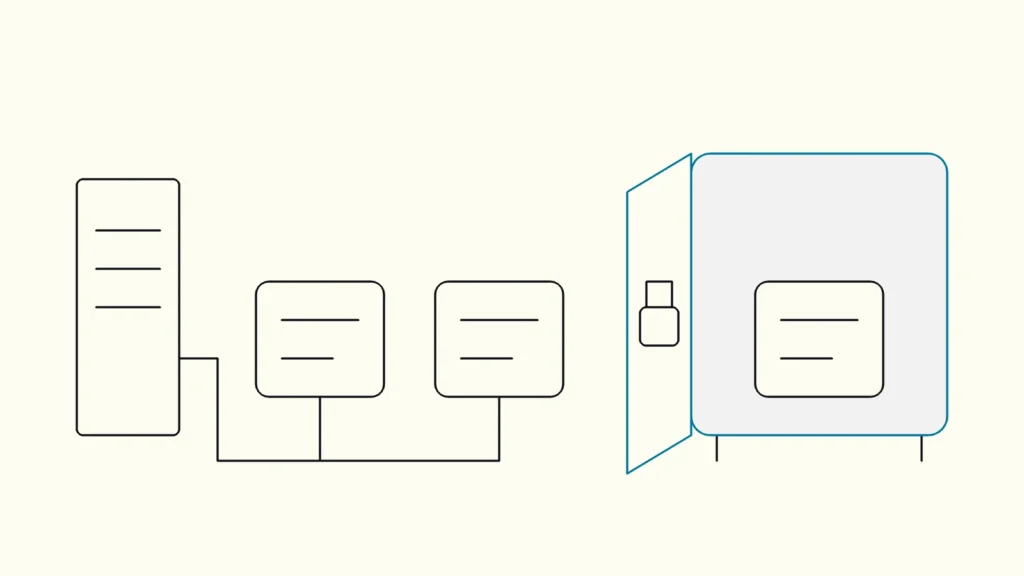
- Add one offline or immutable copy. Use object storage with a retention lock, a vault with immutability, or media that is physically disconnected. Many vendors now describe this as 3-2-1-1-0: one isolated copy and zero errors in restore tests.
- Separate the backup identity. Backup administration should use accounts outside the main directory, with phishing-resistant MFA and no standing access from ordinary admin workstations. The principles are covered in identity and access management explained.
- Protect the backup platform itself. Patch it, restrict network access, require multi-person approval or delays for deleting backups and shortening retention, and alert on such changes.
- Back up more than data. Include system configuration, infrastructure-as-code repositories, golden images, and the identity provider's configuration, since you need them to rebuild.
- Keep enough history. Attackers often sit in networks for weeks. Keep restore points far enough back to predate the intrusion.
- Encrypt backups and keep the keys where an attacker in the main environment cannot reach them.
- Test restores on a schedule. Restore whole systems, not single files, and measure the time against the RTO.
How should you test recovery?
Test recovery by restoring complete systems in an isolated environment and timing the result against your recovery objectives, because a successful backup job says nothing about a successful restore.
A practical testing rhythm:
- Monthly: automated restore of a sample of files and databases, with integrity checks.
- Quarterly: full restore of one critical system into an isolated network, timed from start to a working application.
- Yearly: a tabletop or live exercise for a scenario where the main environment, including the directory, is unavailable. Walk through the order of rebuilding: network, identity, core systems, then the rest.
Record what slowed you down: missing documentation, licence keys stored on the encrypted server, a dependency on a system that was itself down. NIST SP 1800-25, the NCCoE practice guide on protecting data integrity against ransomware and destructive events, describes the components of such an architecture in more detail. The recovery steps should be part of your incident response plan, stored where you can open it when your own systems are down.
What about SaaS and cloud data?
SaaS and cloud data need their own backup decisions, because providers protect their platform against their failures, not your data against your mistakes or a compromised admin account.
Check for Microsoft 365, Google Workspace, CRM systems and source code hosting:
- What the provider's native retention actually covers, and for how long.
- Whether a deleted or encrypted mailbox, site or repository can be restored by you, and how quickly.
- Whether a third-party backup to a separate account or provider is needed for critical data.
The same thinking applies to infrastructure in the cloud: keep backups in a separate account or subscription with separate credentials and retention locks.
Backups are also a compliance matter. As of October 2026, NIS2, Directive (EU) 2022/2555 lists business continuity, including backup management and disaster recovery, among the cybersecurity risk-management measures for covered entities; in Sweden the Cybersecurity Act (cybersäkerhetslagen) requires continuity and crisis management (chapter 2, section 3) but does not name backups itself. Read NIS2 and the Swedish Cybersecurity Act in practice for the wider picture. Good ransomware protection (ransomware skydd) depends on this layer more than any other.
Keep reading
From our work
 Client Case: ZenseactHow Devies helped Zenseact make cybersecurity a natural part of developing safety-critical software for driver assistance and autonomous driving.Read the case
Devies
Want a second opinion?
Devies, a Gothenburg-based product and engineering consultancy, works on questions like this with Nordic product and IT teams. Tell us where you are and we will suggest a sensible first step.
Frequently asked questions
Is the 3-2-1 backup rule still enough?
Not on its own. The 3-2-1 backup rule spreads copies across media and locations, which protects against hardware failure, fire and accidents. It does not require any copy to be offline or immutable, so ransomware with stolen administrator credentials can still reach and destroy all three. Add at least one offline or immutable copy, separate backup credentials with MFA, and regular restore tests.
What is an immutable backup?
An immutable backup is a copy that cannot be modified or deleted by anyone, including administrators, until a defined retention period has passed. Cloud object storage with retention locks and many backup appliances offer this. It protects against attackers who gain administrative access and try to delete backups. Check that retention periods are long enough to predate a possible intrusion and that they fit your data protection obligations.
How often should we test backup restores?
Automate small restore checks at least monthly, run a full restore of a critical system each quarter, and hold a yearly exercise in which you rebuild without your main directory or network. Time every test against your recovery time objective. Many organisations discover only during a real incident that a restore takes days instead of hours, or that a key dependency was never backed up.
Do we need to back up Microsoft 365?
Microsoft 365 includes retention and recovery features, but they are designed for service continuity and limited recovery windows, not as a full backup under your control. If a compromised admin account deletes or encrypts mailboxes, OneDrive files or SharePoint sites, native recovery options may not be enough. Assess retention settings, recovery times and legal requirements, and use a separate backup for critical data where gaps remain.